Device Trust and Access Management

Device trust and access management for the workforce.

From the first day a user joins to every application they need, give your workforce the right access on the right device, at the right time, with the right level of privilege. Keep it all connected as the workforce changes.

OneIdP
Workforce Identity Security

The pillars that make access work.

Identity Management

Identity Management

Manage workforce identities, directories, groups, and identity-provider integrations.

Cloud Directory Identity Integration ADFS User & Group Management Identity Federation
Access Management

Access Management

Apply access policies based on sign-in context, device trust, and authentication requirements.

Continuous Access Evaluation Context-Aware Access Device Authentication Multi-factor Authentication
Privileged Access Management

Privileged Access Management

Grant temporary admin privileges, secure local administrator passwords, and maintain audit trails.

Just-in-Time Privileged Access Local Administrator Password Management
Single Sign-On

Single Sign-On

Give users one branded sign-in to work apps, with passwordless authentication and app-specific access policies.

Passwordless Authentication Enterprise SSO Extended Access Policies (XAP)
Identity Lifecycle Management

Identity Lifecycle Management

Automate provisioning and deprovisioning across connected applications as workforce identities change.

SCIM User Provisioning SCIM User Deprovisioning Attribute Mappings Group Synchronization
Identity Management

Make identity work for the workforce.

Your workforce is always changing. Keep identities up to date and your organization aligned as people join, move, and change roles.

illus_cloud_directory
Cloud Directory

Cloud Directory

Bring users into one central directory with your own domain or a custom OneIdP domain. Keep identity, user information, and authentication organized in one place.

illus_user
User & Group Management

User & Group Management

Organize users into groups, keep their information up-to-date, and manage them from one place. Give every team, role, and assignment the structure it needs.

illus_user_lifecycle
User Lifecycle Management

User Lifecycle Management

Automate user provisioning and deprovisioning, and keep identity data up-to-date. Track account activation so onboarding keeps moving.

illus_identity_integration
Identity Integration

Identity Integration

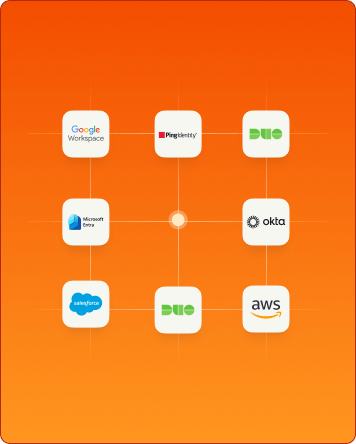
Connect and sync users from Microsoft Entra, Google Workspace, Okta, PingOne, Active Directory, OpenLDAP, and other SAML 2.0 sources, with automatic user matching and migration.

illus_federation
Identity Federation

Identity Federation

Let users authenticate with existing identity provider credentials while OneIdP connects them to the access they need, without creating a second password for the same identity.

illus_adfs
ADFS

ADFS

Extend OneIdP to ADFS-based applications and on-premises services, connecting your existing identity environment with the cloud.

Make the device part of the access decision.

Access Management

Where access meets the context.

Enable seamless & secure access for your workforce to all the apps they need. Stay informed about every access attempt.

Continuous Access Evaluation

Continuously check device compliance and adjust access when its security state changes, so yesterday’s trusted device doesn’t become today’s blind spot.

Device Authentication

Authenticate users directly at the endpoint login screen through OneIdP or existing IdP credentials, with device trust and compliance built into the sign-in decision.

Multi-Factor Authentication

Strengthen logins with OTP from OneIdP Authenticator, third-party authenticator apps, email, or another managed device, including support for offline authentication.

Audit Logging & Reporting

Monitor identity and access activity, investigate incidents, and export detailed records whenever you need them.

Context-Aware Access

Factor in signals such as device, browser, location, IP, Wi-Fi, date, and time to make more informed access decisions.

Privileged Access Management

Privilege, when the work calls for it.

Make privileged work faster to execute and easier to govern. Give employees the access they need while keeping administrator credentials secure across the workforce.

Just-in-Time Privileged Access

Let standard users run approved applications with admin privileges, with time-bound elevation that automatically ends when the configured period is over.

Local Administrator Password Solution

Keep administrator credentials unique, regularly rotated, and centrally managed across Windows and macOS, strengthening the security baseline across every endpoint.

Access Summary & Activity Logs

See who elevated, when, why, and on which device, with activity details and exportable reports that give you a clear record for review and audit.

privileged access management

Bring device trust into the access decision.

Single Sign-On

One-click login for
your workforce.

Give your employees one-click access to work apps while keeping authentication centralized, secure, and simpler to manage.

Passwordless  Authentication

Passwordless
Authentication

Provide employees faster, more secure access to SSO-enabled apps and corporate email on Scalefusion-managed devices, with access backed by device posture and predefined policies.

Extended Access  Policies (XAP)

Extended Access
Policies (XAP)

Make the work app access request earn its way in. Check device compliance, IP, location, app status, OS & updates, and grant access only when the required conditions align.

Access features
User Portal

User Portal

Centralize approved work apps into one branded portal, with a layout that fits your teams. Give employees one place to find and launch apps, with one-click sign-in for supported SSO configurations.

Enterprise  Application SSO

Enterprise
Application SSO

Let your workforce sign in once and stay in the flow, while you keep a close eye on what sits behind that login with device trust, browser checks, and MFA.

Identity Lifecycle Management

Make identity changes travel further.

Bring workforce changes through to every system that depends on them, keeping onboarding, role changes, and offboarding moving at the pace of the business.

Conditional Access

SCIM Inbound

Sync workforce changes into OneIdP automatically as users and groups are added or updated in connected identity, keeping your directory up-to-date and ready for user provisioning.

SCIM Outbound

Carry identity changes from OneIdP into connected applications and directories, keeping onboarding, role changes, and offboarding current wherever those identities are used.

Integrations

Integration with leading identity providers

Seamlessly integrate with leading identity providers such as Okta, Microsoft Entra (formerly known as Azure AD), and Google Workspace. Import your users without needing to create directories and user identities from scratch.

OneIdP

The right access for your workforce starts with device trust.

Trending videos

Video

What is single sign-on?

Watch video

Video

Secure email access on UEM managed devices

Watch video

Video

Entra SSO configuration with Scalefusion OneIdP

Watch video

Video

Secure email access on UEM managed devices

Watch video

Video

What is conditional access?

Watch video

Video

Centralized user portal for SSO

Watch video

Video

Google Workspace configuration with Scalefusion OneIdP

Watch video

Frequently asked questions

Yes. OneIdP integrates with identity sources such as Microsoft Entra, Google Workspace, Okta, PingOne, Active Directory, and OpenLDAP. Use supported identity federation to connect your existing setup and simplify workforce authentication without rebuilding your identity environment from scratch.

Get a Demo